Bring a Forge account over as drafts, then adopt the real servers.
A read-only Forge API token is enough. SrvYard lists your organisations’ servers, reads the ones you tick, and shows a plan: sites, deploy scripts, daemons, scheduled jobs, databases and firewall rules. Forge itself is never written to, and no server is changed.
# the Forge API of your organisations
token       forge.laravel.com/profile/api
abilities   read only; .env needs site:manage-environment
checked     with one call, kept encrypted for an hour
servers     organisation / server, you tick which
env files   only if you ask
scripts     shown beside their translation, never run
forge untouched01What you need
02How it goes
import, then scan, then adoptImport
Open Import / migrate, choose Laravel Forge, paste the read-only token and press Verify and continue. One read call checks it.
Pick servers
Tick the servers to read. Each site costs several calls to the other panel’s API, so a big account takes a few minutes. Reading
.envfiles is a separate switch, off by default.Review the plan
Totals of new drafts, updates and skipped items, then a card per server with a tick box for every site, daemon, scheduled job, database and firewall rule. Deploy scripts appear beside their translation.
Create the drafts
Tick that you read the deploy scripts, choose whether to delete the token (recommended) and press Create drafts. Nothing is installed.
Connect, scan, adopt
Connect the real server, scan it, and adopt what the scan found. Deploy once from SrvYard, check domains and certificates, and only then change DNS.
03The import screen
from the demo organisation
04What the import reads and what it creates
all of it read-only| Read from Laravel Forge | Becomes in SrvYard |
|---|---|
| Servers of each organisation you can see | A custom server that awaits access, named and addressed like the Forge one |
| Sites, their domains and repository | A site marked Needs provisioning, with its domains and redirects |
| Deploy script of each site | A draft script, translated, with a verdict per line |
| Background processes | Daemons |
| Scheduled jobs | Scheduled jobs |
| Databases and database users | Database records (no passwords) |
| Firewall rules | Firewall rules, applied only when you apply them to a connected server |
| SSH key names | Names only |
| Nginx templates and organisation recipes | Nginx templates and recipes |
| Basic-auth rules, certificates, the site Nginx configuration | Read as metadata or text for the review; certificates are not copied |
The .env of each site, if you asked | Key names, and values only if you tick them per site |
Drafts, not machines
Servers become custom servers awaiting access, sites say Needs provisioning, and daemons, scheduled jobs, databases and firewall rules are records that are applied once the server is connected. Every item is tagged with the panel’s name. Nothing touches a machine and nothing is written to Laravel Forge.
Deploy scripts
Each line is shown with a verdict: unchanged, translated (a variable renamed, or a step SrvYard does itself removed), review (an old absolute path, a variable SrvYard does not have) or unsupported (commented out: anything that needs sudo, or restarts Supervisor). The script is never run by the import; it runs only at a deployment you start.
05What is never copied
because the API will not give it to you- Database passwords, SSH private keys, storage provider secrets and Git tokens. No Forge API returns them.
- The public key text of server SSH keys: Forge lists names only.
- Passwords of HTTP basic-auth rules.
Environment files are read only if you switch it on, and imported only for the sites you tick; without that, key names alone can be shown. The token and everything read with it are encrypted, expire after an hour and are deleted when you finish or cancel. Delete the token in Laravel Forge too.
How your data is handled during an import is also spelled out on the security page.
06Then scan and adopt the real server
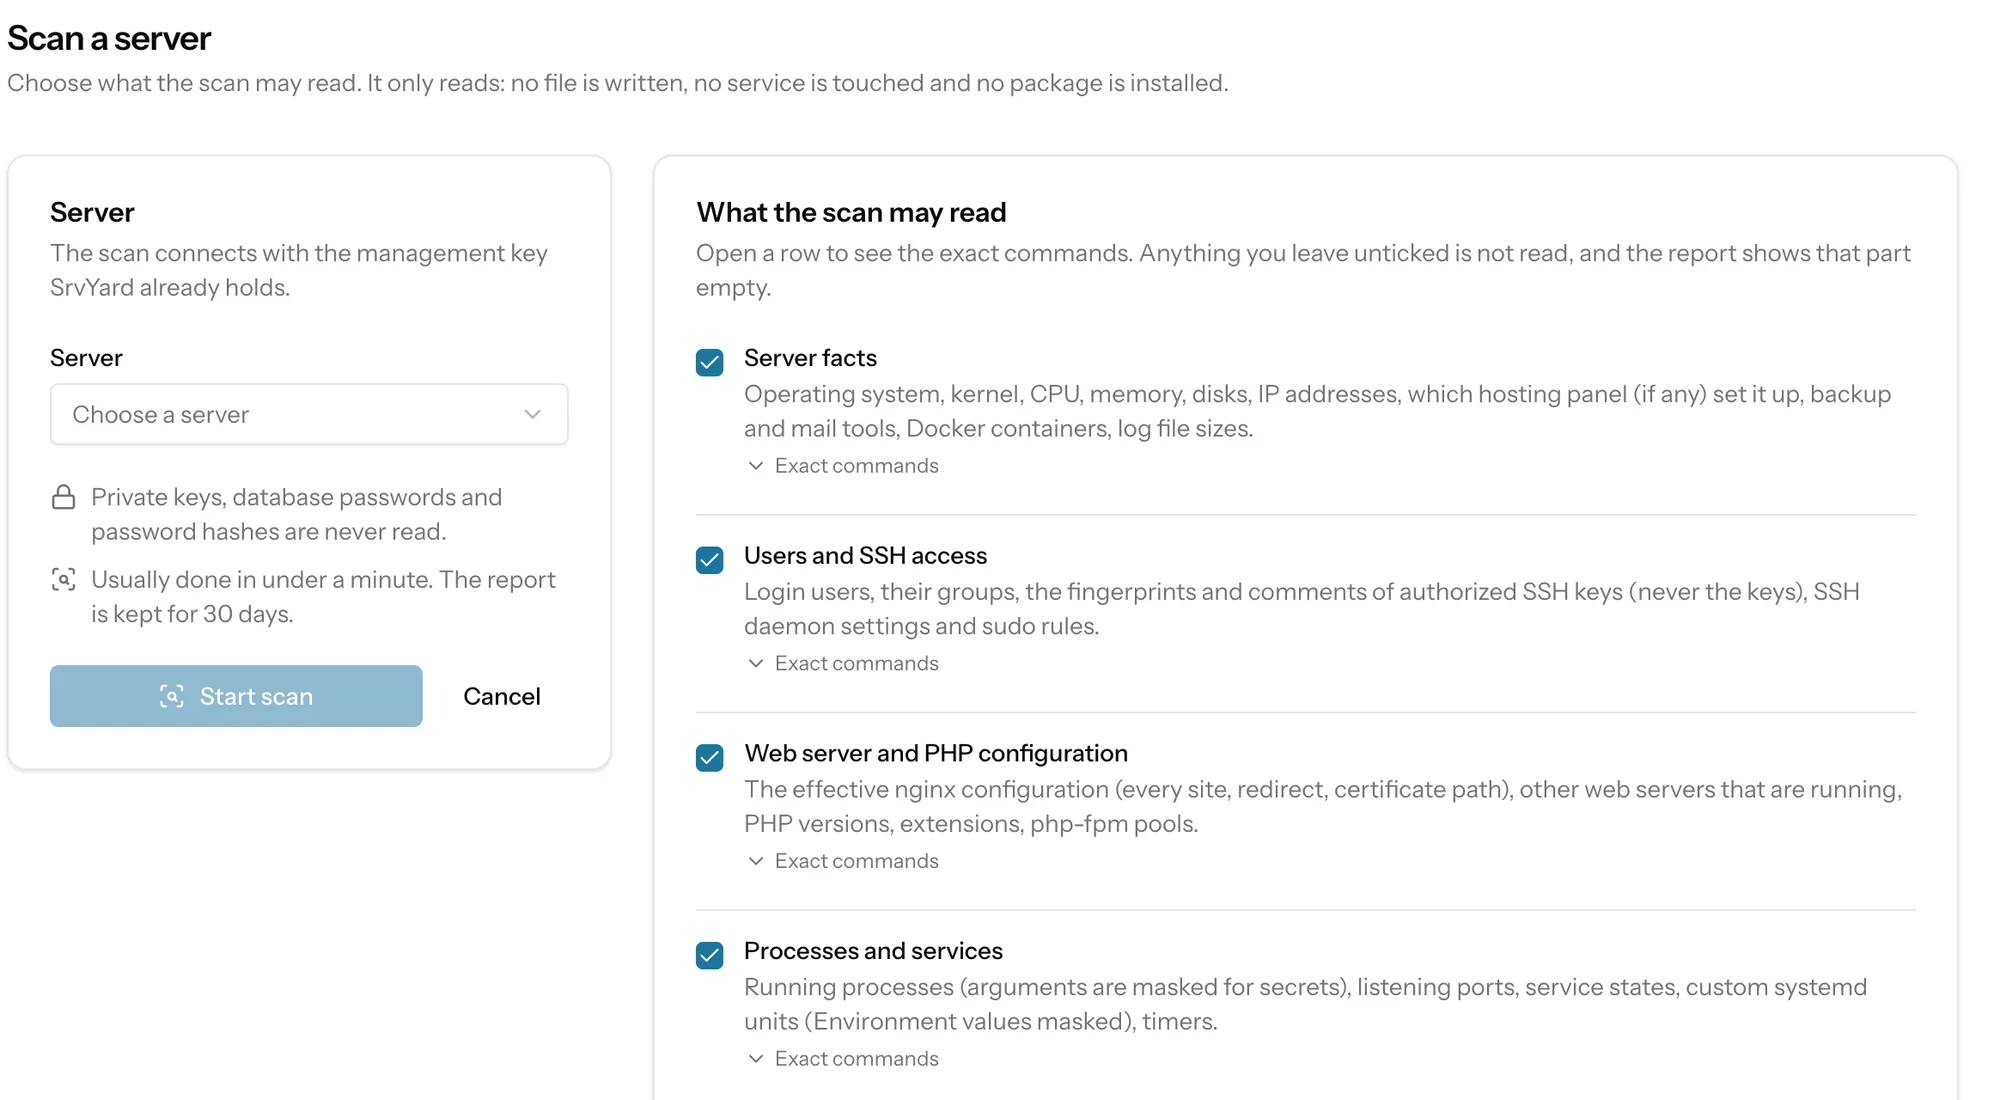
the half that reads the machineForge leaves recognisable marks: a forge user, an Nginx forge-conf include folder and a releases, current and shared layout. The scan recognises the panel and the layout, so the report can adopt a Forge site without moving files.
The scan is read-only. You choose what it may read, and every consent lists its exact commands. Private keys, database passwords and password hashes are never read. Adopting registers each site where it already is, in observe mode: SrvYard writes nothing to the web server, keeps a restore point, and can roll back.
Sites deployed through Envoyer may show an empty deploy script, and the review says so. A part the token cannot read (for example without the environment ability) is skipped with a warning under Things to know before you apply.
07Switching the old panel off
a guide, never run for youForge has no agent on the server. It reaches the machine over SSH with its own keys, so the guide has you remove those keys, then the sudo rules, and decide about Forge’s housekeeping cron lines.
Things the guide flags: Forge renews the certificates it issued, so issue a SrvYard certificate for any site whose certificate nothing else renews; deploy webhooks at GitHub, GitLab or Bitbucket still point at Forge; and do not change the database passwords Forge knows while Forge is still attached. Keep the forge Linux user (the sites run as it) and Nginx as it is.
SrvYard shows a detach guide per panel after adoption. Every command in it is for you to read and run; SrvYard never executes it. Keep the old panel running a few days as a safety net, then cancel it.
Adoption in depth: Adopt a site that is already on your server.
08Questions
answers from the docsWhat does the Forge token need?
Only read access to servers and sites, from forge.laravel.com/profile/api. To also read .env files it needs the site:manage-environment ability. See Migrate from Laravel Forge, Ploi or VitoDeploy.
Does the import change anything in Forge or on my servers?
No. It only reads, and creates drafts in SrvYard: servers wait for access and sites say Needs provisioning. Delete the token in Forge when you finish.
What can SrvYard not copy from Forge?
Database passwords, SSH private keys, storage provider secrets and Git tokens, because no API returns them, plus the public key text of server SSH keys and basic-auth passwords.
Import one Forge site. Keep Forge running until it works.
Free: 1 server, 3 sites, 100 deploys a month. Read the docs first if you prefer.